Setting up SSO via a Microsoft Entra ID enterprise application
Configure SAMLSAML An XML-based standard for exchanging authentication and authorization data between an identity provider and a service provider. Process360 Live supports SAML 2.0 for SSO. SSOSSO An authentication scheme that lets users sign in once with an identity provider and access Process360 Live without re-entering credentials. for an on-premises iGrafx platform using a Microsoft Entra ID (formerly Azure AD) enterprise application.
These steps apply to the iGrafx platform Datacenter Edition (on-premises) only. For the cloud solution, follow the Legacy SAML setup guide instead.
Prerequisites
- A SAML keystore set up, with the keystore details in
igrafx.properties. - Access to Enterprise applications in the Azure portal.
Steps
-
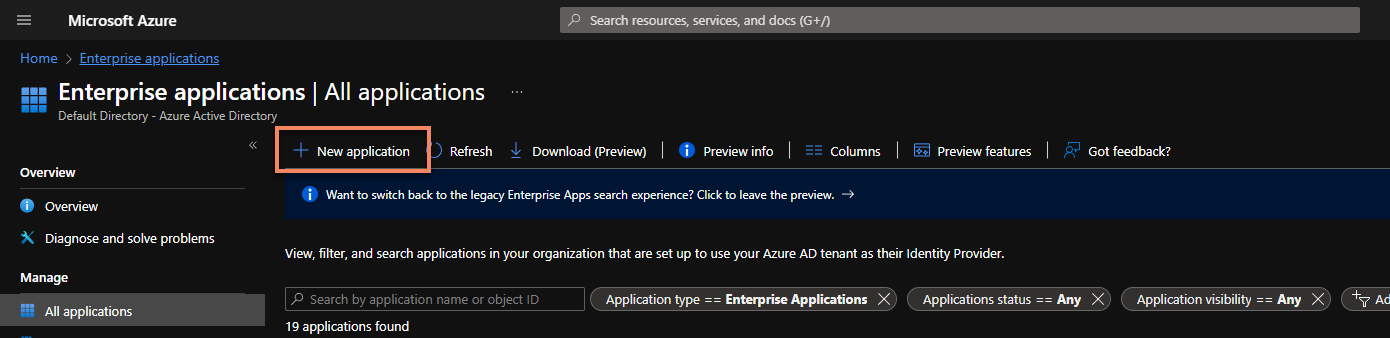
In the Azure portal, go to Enterprise applications and select New application.
-
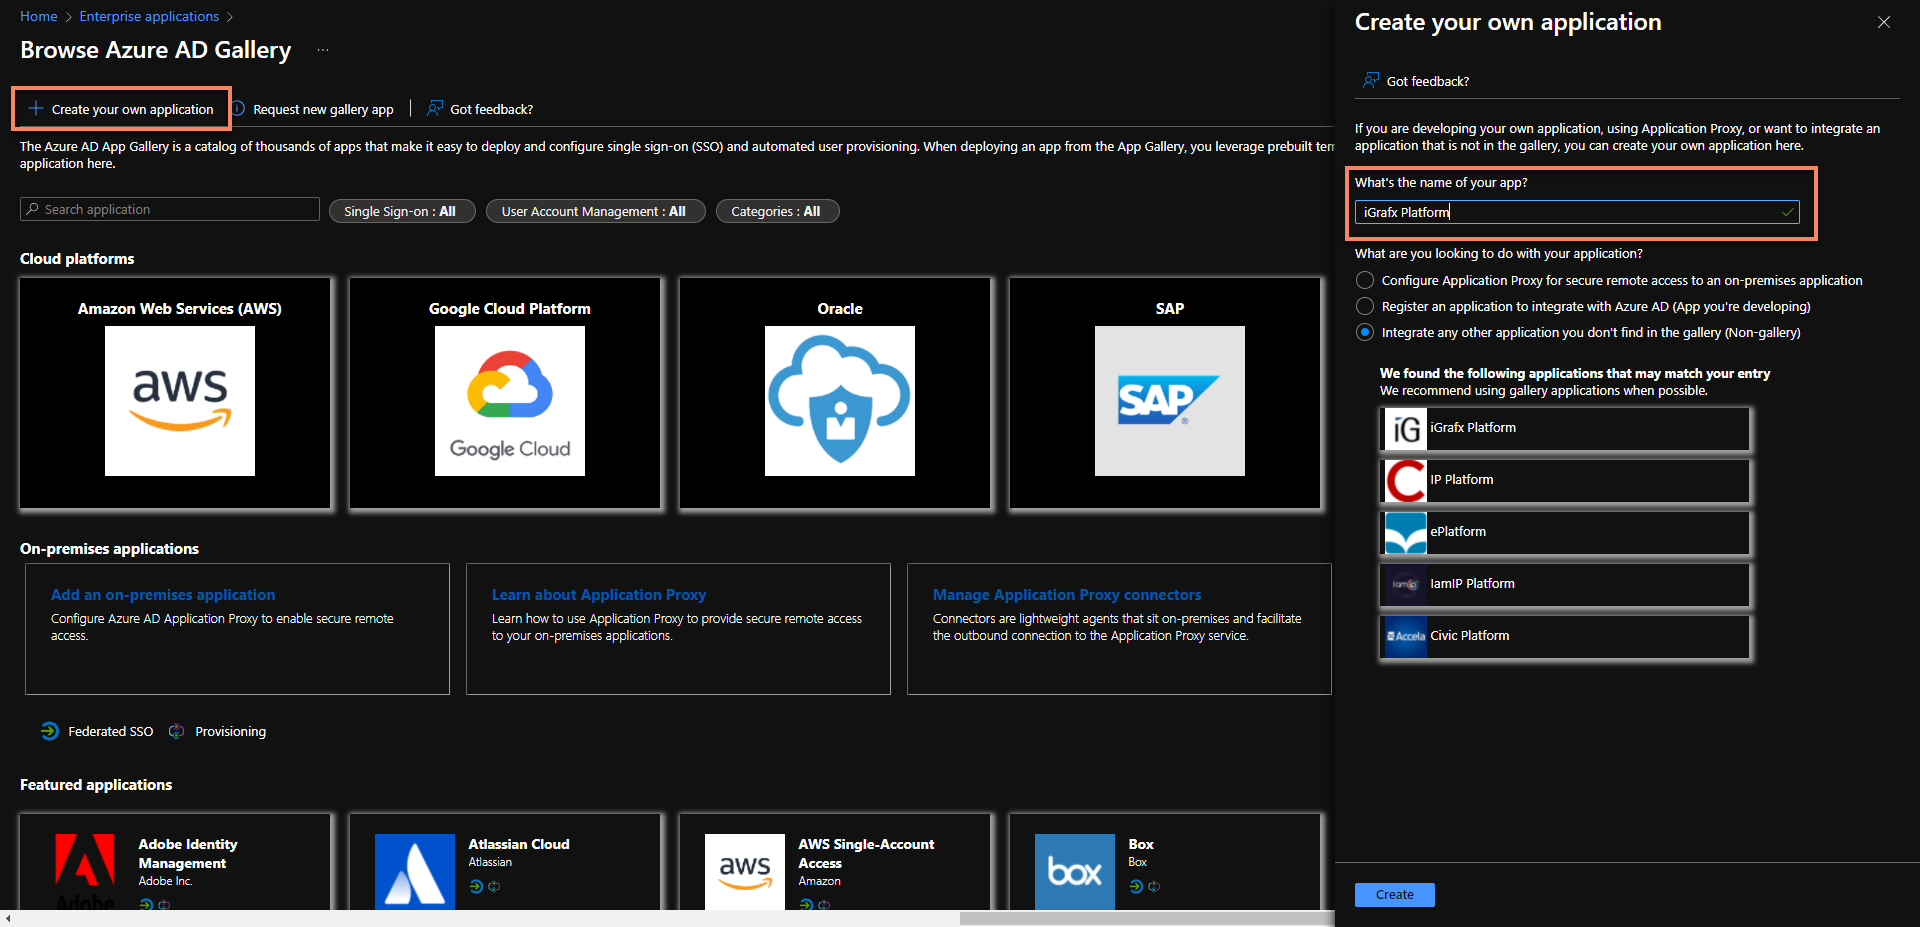
Click Create your own application, enter a name, and click Create.
-
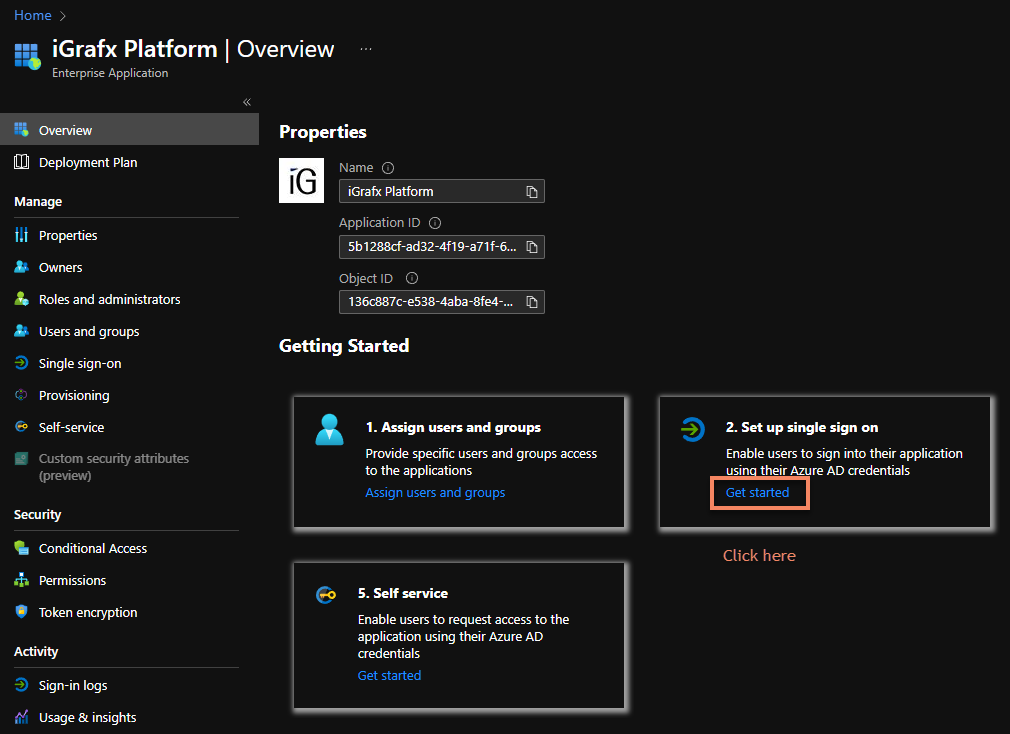
Select Get started.
-
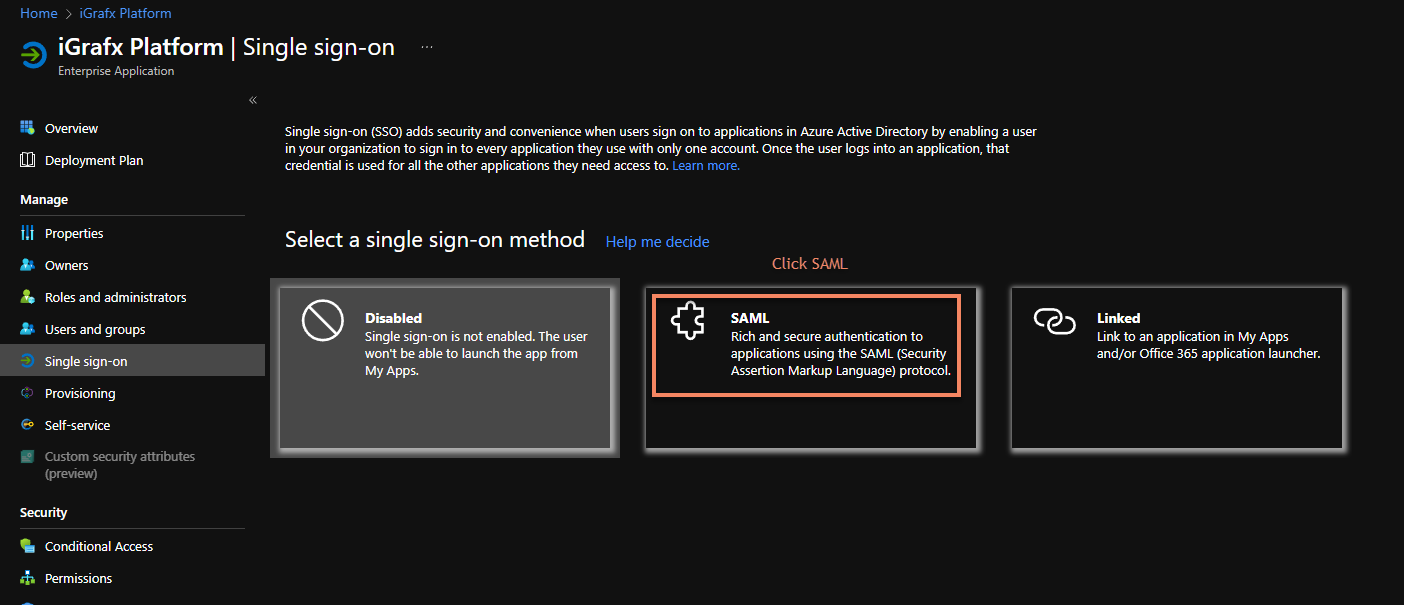
Select SAMLSAML An XML-based standard for exchanging authentication and authorization data between an identity provider and a service provider. Process360 Live supports SAML 2.0 for SSO..
-
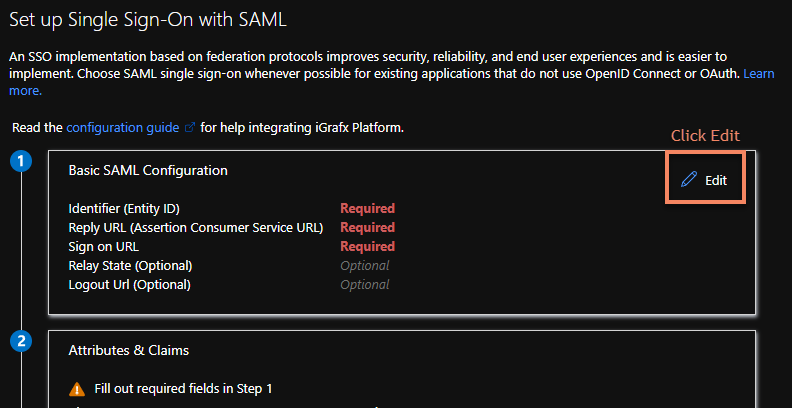
Select Edit on the basic SAMLSAML An XML-based standard for exchanging authentication and authorization data between an identity provider and a service provider. Process360 Live supports SAML 2.0 for SSO. configuration.
-
Select Add identifier and enter your platform URL with
/saml/metadataappended. Add the Reply URL as your platform URL with/saml/SSO, and add the Sign on URL.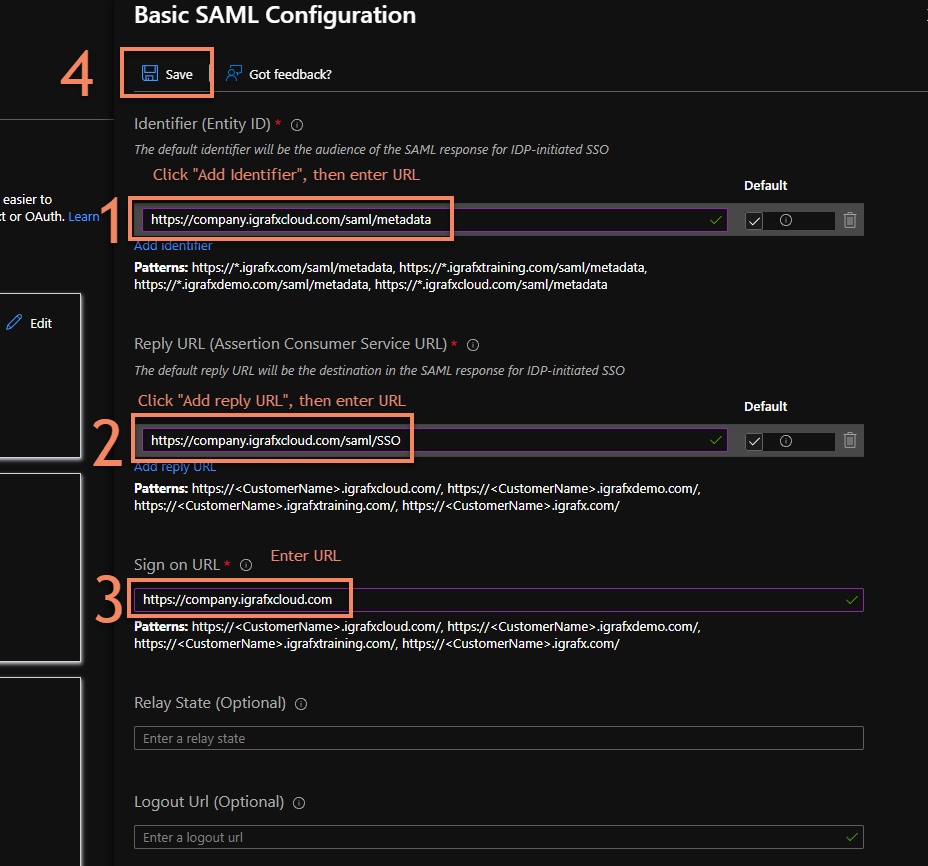
-
Click Save.
-
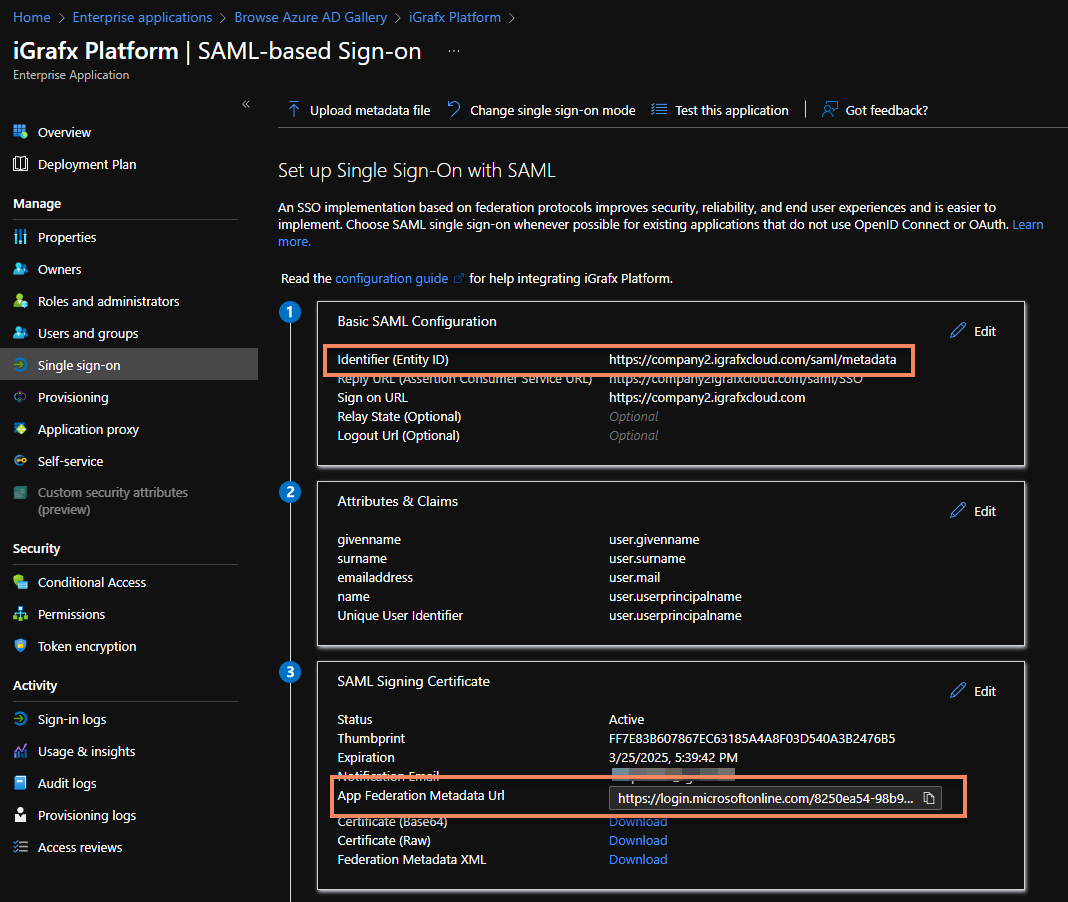
Copy the App Federation Metadata URL.
-
On the Users and groups tab, assign the users and groups who sign in to iGrafx.
-
In the platform, go to Administration → User Management → SAMLSAML An XML-based standard for exchanging authentication and authorization data between an identity provider and a service provider. Process360 Live supports SAML 2.0 for SSO., select Update Identity Provider Metadata, and add the metadata URL.
-
Activate the
samlsecurityprofile — see Configuring authentication. -
Confirm
samlKeystore.jksis set up and its access details are inigrafx.properties— see Set up a SAML2 keystore. -
Restart the platform.
-
Make sure your NameID (in the Attributes & Claims section) matches the login name of your users in the platform.
-
If issues arise, follow the debugging steps.